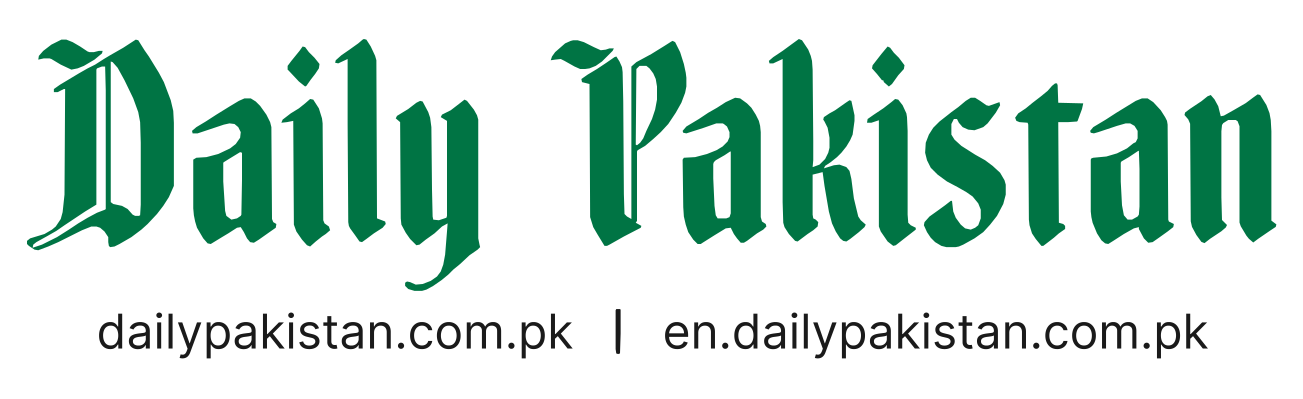
LONDON – Hackers drained staggering $6.3 billion from Binance, sending shockwaves through the global crypto industry. As suspicions turn toward North Korean-linked hackers, major exchanges including Coinbase and Kraken are scrambling to tighten security.
Binance breach exposed critical reality confronting the cryptocurrency industry as attackers took minutes to steal assets worth billions, while investigators can spend weeks or months attempting to trace the money. Although Binance has promised to cover the financial losses, the attack has placed rival exchanges under pressure to demonstrate that their own security systems can withstand similar threats.
A security emergency jolted global cryptocurrency industry, forcing major exchanges, including Coinbase and Kraken, to reinforce their defenses amid growing fears of sophisticated attacks linked to North Korean hackers.
The unprecedented theft, carried out largely within just 20 minutes on Thursday, exposed alarming weaknesses in the digital asset ecosystem and raised a troubling question: If hackers can penetrate the world’s largest cryptocurrency exchange, how secure are billions of dollars held on other trading platforms?
The attack prompted cryptocurrency companies to review their security infrastructure, strengthen internal safeguards and push for an industry-wide emergency response system capable of stopping stolen digital assets before they disappear. The incident also reignited concerns over whether the rapidly expanding cryptocurrency industry is sufficiently prepared for the cybersecurity risks accompanying its deeper integration into mainstream finance.
Blockchain intelligence firms TRM Labs and Chainalysis found that hackers transferred the majority of stolen $6.3 billion in approximately 20 minutes, exploiting vulnerabilities in the infrastructure responsible for authorizing cryptocurrency withdrawals. The breach forced Binance to temporarily suspend withdrawals as its security teams scrambled to investigate unauthorized transactions and contain further losses.
Binance co-CEO Richard Teng called incident highly sophisticated operation, revealing that investigators initially suspected hackers had compromised a software engineer’s laptop. However, the investigation subsequently uncovered additional points of unauthorized access, indicating that the operation was considerably more complex.
The attackers deployed malicious software designed to erase evidence of their activities, complicating efforts to trace their movements through the company’s systems. Despite massive financial damage, Binance assured customers that their funds remained safe and pledged to absorb the losses through company resources and its user-protection reserve.
The security shock quickly spread beyond Binance, prompting competing cryptocurrency exchanges to reassess their defenses. Coinbase, one of the largest US cryptocurrency trading platforms, confirmed that it had introduced precautionary adjustments to systems responsible for protecting digital asset keys stored offline.
These cold-storage mechanisms are intended to shield cryptocurrency holdings from internet-based threats. Although Coinbase did not report being compromised in the Binance attack, the company said the changes were made as an additional precaution.
Kraken also confirmed that it was closely following developments surrounding the breach and examining lessons that could strengthen its existing security arrangements.
The response illustrates how single major exchange breach can trigger security reviews throughout the wider cryptocurrency sector, even among platforms that were not directly affected.
Attention increasingly turned toward North Korean-linked hacking groups as blockchain investigators examine the origins of the attack. TRM Labs and Chainalysis identified patterns resembling previous large-scale cryptocurrency thefts attributed to North Korean cybercriminals. Investigators linked operation to suspected North Korean hacking activity, although the precise identities of those responsible have not been conclusively established.
While Binance struggled to contain the breach, major stablecoin issuers launched efforts to block the movement of suspected stolen assets. Tether froze approximately $1.57 billion connected to the attack, while Circle restricted another $800 million.
The combined action covered roughly $2.37 billion in cryptocurrency, representing a significant portion of the funds targeted in the heist. Additional asset-freezing efforts by other industry participants brought the total identified or frozen amount to approximately $3 billion, according to Binance’s reported figures.
The attack intensified calls for cryptocurrency companies to abandon isolated approaches to cybersecurity and adopt coordinated industry-wide defenses. Officials proposed establishing real-time warning system that would immediately notify major exchanges and relevant companies whenever a significant cyberattack is detected.
Such a network could allow participating platforms to rapidly identify suspicious wallets, share intelligence, coordinate investigations and temporarily restrict transfers of suspected stolen assets where technically and legally possible.
The urgency comes as US regulators under President Donald Trump’s administration promote greater integration of cryptocurrency markets into the conventional financial system. As digital assets become more closely connected with mainstream investment and banking activities, major cyberattacks could carry increasingly serious consequences for market confidence.
Is North Korea’s Lazarus Group behind massive $6.3 Billion Binance Hack?